Design Legal AI Agents That People Can Check and Control
Map what an AI agent should do, which records it may use, and where a lawyer or administrator must approve actions. Use Claude Code as one possible technical building block—not a substitute for legal oversight.
Save or follow this source
Add AdvocateRahulDev.com to Google Preferred Sources or open this page in your preferred AI tool.
- Map data, tools and approval points
- Separate draft-only from external actions
- Test failure handling before rollout
What Would a Safe Legal AI Agent Need?
Explain your intended legal task, who will review the result and any data-access constraints. An initial consultation can define the next decision without promising a particular outcome.
Review My Agent DesignWhat Could Work Better?
Map what an AI agent should do, which records it may use, and where a lawyer or administrator must approve actions. Use Claude Code as one possible technical building block—not a substitute for legal oversight. The starting point is the current way the work is carried out, who is responsible and which documents are permitted for any trial. A decision should identify value alongside professional and technical limitations.
How We Could Approach Your Requirements
We can discuss the intended outcome, current systems, relevant source material, approval roles and what a bounded evaluation would need to establish. Any engagement scope or deliverables must be agreed separately; these descriptions are examples of areas for review, not claims of an existing partnership, certification or guaranteed result.
For law-firm website and client-discovery work, the project-approved connected service destination is Councl for Law Firms. Its scope should be evaluated independently of the legal-AI work described here.
Explore Councl for Law FirmsCheck Every Step Before Connecting Live Systems
Clarify the people, documents, tools, source evidence and controls relevant to a manageable test. Discuss the proposed checks before moving from a demonstration to an approved working process.
Discuss Agent Safety GatesTechnology and Legal Practice: A Short Overview
This project-approved video gives broader context. The independent evidence-led guide below addresses the specific task and its limits.
Claude Code Legal Agent Architecture: Components, Evidence and Approval Gates
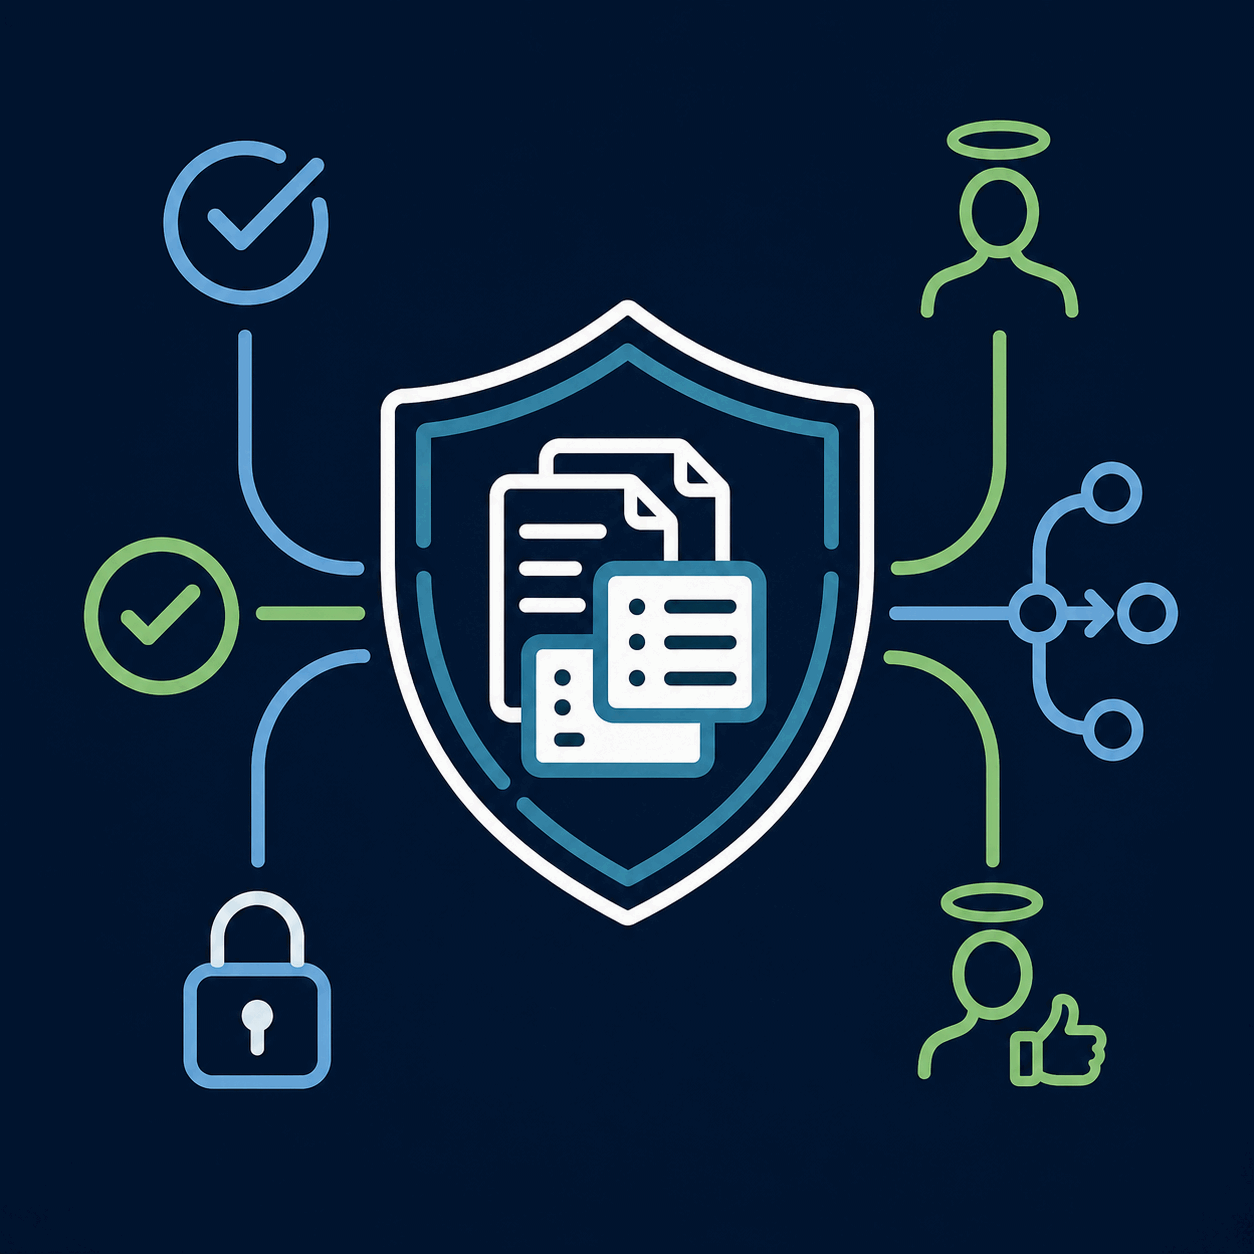
A reviewable legal AI agent architecture separates the request, identity and permissions, permitted sources, task planning, model-assisted processing, validation, human approval and monitoring. Claude Code may help implement components, but permissions and tests must be verified in the actual environment. No agent should send legal advice, modify records or act externally without explicitly authorized controls.
This is a proposed technical reference for legal teams building agents. It is not a finished or independently tested system design. Real deployments must be tailored to the legal system, organizational policies and architecture of connected products. The sections describe independently necessary controls rather than representing a vendor security certification.
Author: Dr. Rahul Dev: PhD Data Scientist, Technology Law & Patent Attorney, and AI Educator with 20+ years advising global CEOs and CXOs on tech, business, and legal innovation.
Layer one: request intake and matter identity
Every agent invocation should begin with a clearly scoped user request, an authenticated identity and a matter or project context. The system must identify whether the user wants a draft, information retrieval, a report or a consequential action. A matter label in natural language does not establish access permission by itself; identity should be checked through the systems controlling the records. Store the intended task, the permitted data category and the reviewer role in a structured request record. If the agent cannot establish context or has ambiguous instructions, it should stop and ask for clarification instead of inferring which client file to open. This boundary makes subsequent review meaningful.
Primary evidence and scope: NIST, AI Risk Management Framework
Layer two: the document and authority source boundary
A legal agent may draw from signed contracts, internal precedents, licensed law sources, public regulator notices or matter records, but these have different rights and reliability. Identify each source, owner, jurisdiction, date and access policy. A retrieval step should return a verifiable passage or document reference, not only a model-generated summary. If the primary source is unavailable, a generated answer should say so instead of substituting recollection. Citation validation is a separate step because even a real document may not support the proposition advanced. Jurisdiction and time context should travel with the passage into any later drafting or decision component.
Primary evidence and scope: American Bar Association, Formal Opinion 512 (29 July 2024); Solicitors Regulation Authority, Misuse of AI — warning notice (17 August 2026)
Layer three: constrained tools and permission scopes
Claude Code can interact with development tools and connected systems subject to technical configuration. The architecture should specify each permitted command, connector action, file directory and account scope. Draft generation and read-only searches should be distinguished from changes to source records, emails, external submissions and file deletion. All higher-impact actions should use explicit approval gates; a general statement that the agent is “human supervised” is insufficient without an identifiable point of control. Test the installed product’s permission behavior under a restricted account and include a revocation mechanism. External data should not be trusted as operational instructions merely because it is retrieved through an approved connector.
Primary evidence and scope: Anthropic, Claude Code permissions documentation; Anthropic, Claude Code MCP configuration
Layer four: task planning with bounded subagents
Breaking a request into smaller analysis steps can make a workflow easier to inspect, but spawning multiple agents can also multiply access and error paths. A possible division is one component that identifies documents, another that extracts target clauses, and a separate reviewer aid that checks source references. Each component should receive only the inputs it requires and write outputs in a known format. Define the maximum task scope, prohibited actions, handling of uncertainty and ownership of shared state. A subagent’s assertion that its job succeeded is not independent verification. The orchestration layer should preserve a trace that shows which component generated each decision-relevant item.
Primary evidence and scope: Anthropic, Claude Code subagents documentation; NIST, AI Risk Management Framework
Layer five: legal validation before action
Validation should include deterministic checks where possible—valid dates, allowed file identifiers, mandatory fields—as well as professional examination of legal substance. For a proposed clause comparison, a lawyer checks whether changes reflect actual source wording and whether exceptions or amendments alter the conclusion. For a legal research response, the reviewer inspects the primary authority and its current treatment. The agent should surface discrepancies, omissions and unsupported statements. Acceptance criteria must be defined for the particular legal task, not adopted from a generic model score. Material errors should produce a hold or escalation state rather than an automated workaround.
Primary evidence and scope: Solicitors Regulation Authority, Misuse of AI — warning notice (17 August 2026); American Bar Association, Formal Opinion 512 (29 July 2024)
Layer six: explicit human approval and external-action gates
Draft generation, internal routing and external action are not equivalent risk categories. Sending client advice, altering a signed agreement record, filing a court document or issuing a legal notice can have consequences that a test script cannot reverse. The design should therefore implement a named approver and an auditable confirmation action for specified changes. An agent should never infer legal approval from the absence of a rejection. The approval record should identify the material reviewed, source context, intended recipient and version. Where authorization has expired or the approver is unavailable, the system should stop and retain the draft for later consideration.
Primary evidence and scope: American Bar Association, Formal Opinion 512 (29 July 2024); Solicitors Regulation Authority, Misuse of AI — warning notice (17 August 2026)
Layer seven: observability, exceptions and rollback
A responsible design records who initiated a task, which sources and tools were accessed, what outputs were produced, where a human intervened and how failures were resolved. These logs need their own access and retention policies; they must not become an uncontrolled archive of privileged data. Define what constitutes an incident, who can disable an agent, how data corrections propagate and how a workflow returns to a manual process. Avoid reporting success solely as the absence of a software exception. Quality monitoring should include a sample of source accuracy, missed exceptions, unauthorized access attempts and user escalation, with a clear process for adjusting the workflow.
Primary evidence and scope: NIST, AI Risk Management Framework; Anthropic, Claude Code security documentation
Architecture review must precede production integration
The seven-layer structure is a proposed analytical model, not a claim that Anthropic requires exactly seven layers. A production design should be evaluated against the organization’s technology, procurement constraints and professional obligations. Map data flows, credentials, source systems, authentication boundaries, approval points, failure states and changes in product capabilities. Compare the draft to actual connector documentation and perform permission tests before wiring it into live client matters. A small offline demonstration can validate input/output handling without demonstrating the legal safety of a full deployment. A separate governance and technical review should authorize every consequential rollout.
Primary evidence and scope: Anthropic, Getting started — Claude for the legal industry; NIST, AI Risk Management Framework
Illustrative Workflow — What a Bounded Test Looks Like
Illustrative architecture walkthrough: an in-house lawyer asks an agent to prepare a first-pass obligations table from fictional supplier contracts. Intake records the request, authorized fictional data set and internal reviewer. A read-only component extracts clauses with document offsets. A separate checker flags missing references and contradictory deadlines. The lawyer reviews each obligation and marks it approved or unresolved. Only approved entries may be exported to a test tracker, and no external email or contract record is modified. The log captures each tool invocation, source pointer and sign-off. If source links cannot be resolved, the system stops. This describes design logic, not a deployed or performance-tested agent.
Practical Decision Checklist
- State one concrete legal or operational task and what a satisfactory result would mean.
- List the source records, permissions, jurisdiction, relevant dates and any client or contractual restrictions.
- Decide what should be tested with fictional or other duly authorized data before wider consideration.
- Name the qualified reviewer for legal substance, the technical owner where relevant, and the stop condition.
- Record evidence, exceptions, unresolved questions, approved next actions and a date to revisit the decision.
Frequently Asked Questions
Can a legal agent make a decision without a lawyer?
A generated recommendation should not be treated as legal authority. Consequential matters require appropriate professional and organizational review.
Why distinguish read-only tools from write actions?
A mistaken answer may be corrected before use; an unauthorized write or external submission can change records or affect others.
Does a seven-layer diagram certify compliance?
No. It is a planning aid. Actual legal and security assessment depends on implemented controls, local rules and tested operations.
Sources, Dates and Limitations
Publisher research review: 29 October 2026. Links below identify product documentation and regulator guidance used for limited claims. Vendor descriptions are statements by their publishers, not independent feature testing. Product access, professional rules and technical settings can change. Commentary on potential workflow design is editorial analysis, not proof of a deployed service.
- NIST, AI Risk Management Framework
- American Bar Association, Formal Opinion 512 (29 July 2024)
- Solicitors Regulation Authority, Misuse of AI — warning notice (17 August 2026)
- Anthropic, Claude Code permissions documentation
- Anthropic, Claude Code MCP configuration
- Anthropic, Claude Code subagents documentation
- Anthropic, Claude Code security documentation
- Anthropic, Getting started — Claude for the legal industry
- Anthropic, Claude for the legal industry (12 May 2026)
- Anthropic, Introducing artifacts for legal work (28 October 2026)
Related Research and Practical Services
Plan a Controlled Legal AI Agent Pilot
Describe what you would like to improve, what has already been tested and what must remain under professional supervision. The next conversation can establish the appropriate scope and supporting evidence.
Discuss My Agent ArchitectureAbout Dr. Rahul Dev
Dr. Rahul Dev is a PhD Data Scientist, Technology Law and Patent Attorney, AI Educator and international business advisor. His work spans artificial intelligence, intellectual property, technology strategy, legal systems and digital growth. The article is educational and does not create an attorney-client or advisory relationship.
Author profile